


[Dec-2023] NSE7_EFW-7.0 Exam Questions and Valid NSE7_EFW-7.0 Dumps PDF
NSE7_EFW-7.0 Brain Dump: A Study Guide with Tips & Tricks for passing Exam
NEW QUESTION # 89
Which configuration can be used to reduce the number of BGP sessions in an IBGP network?
- A. Route reflector
- B. Neighbor range
- C. Neighbor group
- D. Next-hop-self
Answer: A
NEW QUESTION # 90
An administrator has decreased all the TCP session timers to optimize the FortiGate memory usage. However, after the changes, one network application started to have problems. During the troubleshooting, the administrator noticed that the FortiGate deletes the sessions after the clients send the SYN packets, and before the arrival of the SYN/ACKs. When the SYN/ACK packets arrive to the FortiGate, the unit has already deleted the respective sessions .
Which TCP session timer must be increased to fix this problem?
- A. TCP half open.
- B. TCP session time to live.
- C. TCP half close.
- D. TCP time wait.
Answer: A
NEW QUESTION # 91
Which two statements about the Security Fabric are true? (Choose two.)
- A. Only the root FortiGate collects network information and forwards it to FortiAnalyzer.
- B. All FortiGate devices in the Security Fabric must have bidirectional FortiTelemetry connectivity.
- C. Branch FortiGate devices must be configured first.
- D. FortiGate uses FortiTelemetry protocol to communicate with FortiAnalyzer.
Answer: B,D
NEW QUESTION # 92
Refer to the exhibit, which shows a central management configuration.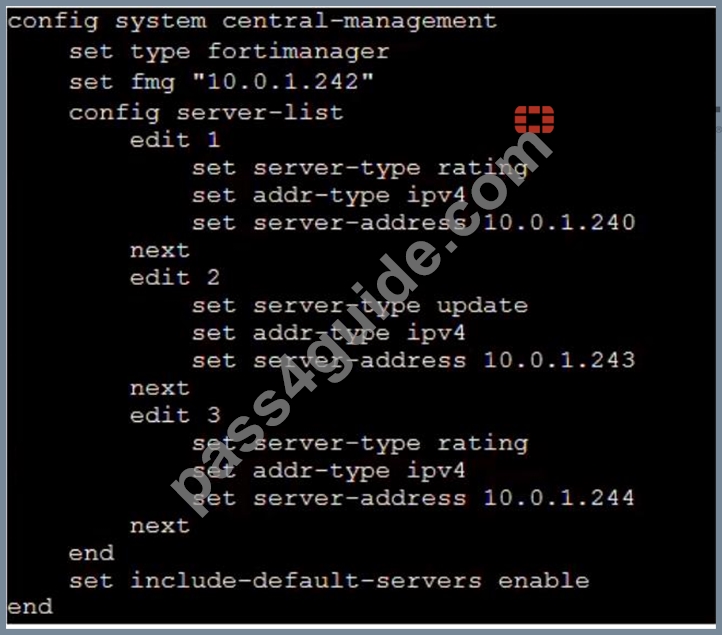
Which server will FortiGate choose for web filter rating requests, if 10.0.1.240 is experiencing an outage?
- A. 10.0.1.244
- B. 10.0.1.242
- C. 10.0.1.243
- D. Public FortiGuard servers
Answer: A
Explanation:
by default,( include-default-servers ) enabled .this allows fortigate to communicate with the public fortiguard servers , if the fortimanger devices (configured in server-list) are unavailable .
NEW QUESTION # 93
Examine the output of the 'diagnose debug rating' command shown in the exhibit; then answer the question below.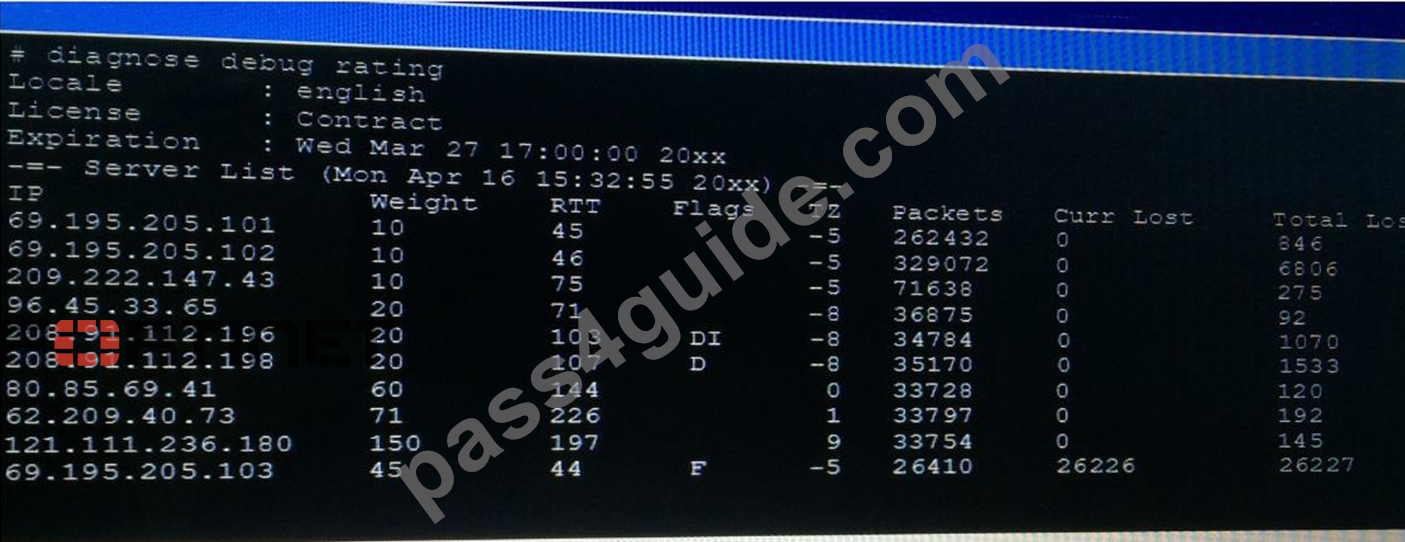
Which statement are true regarding the output in the exhibit? (Choose two.)
- A. There are three FortiGuard servers that are not responding to the queries sent by the FortiGate.
- B. A server's round trip delay (RTT) is not used to calculate its weight.
- C. The TZ value represents the delta between each FortiGuard server's time zone and the FortiGate's time zone.
- D. FortiGate will send the FortiGuard queries to the server with highest weight.
Answer: C,D
NEW QUESTION # 94
View the exhibit, which contains a screenshot of some phase-1 settings, and then answer the question below.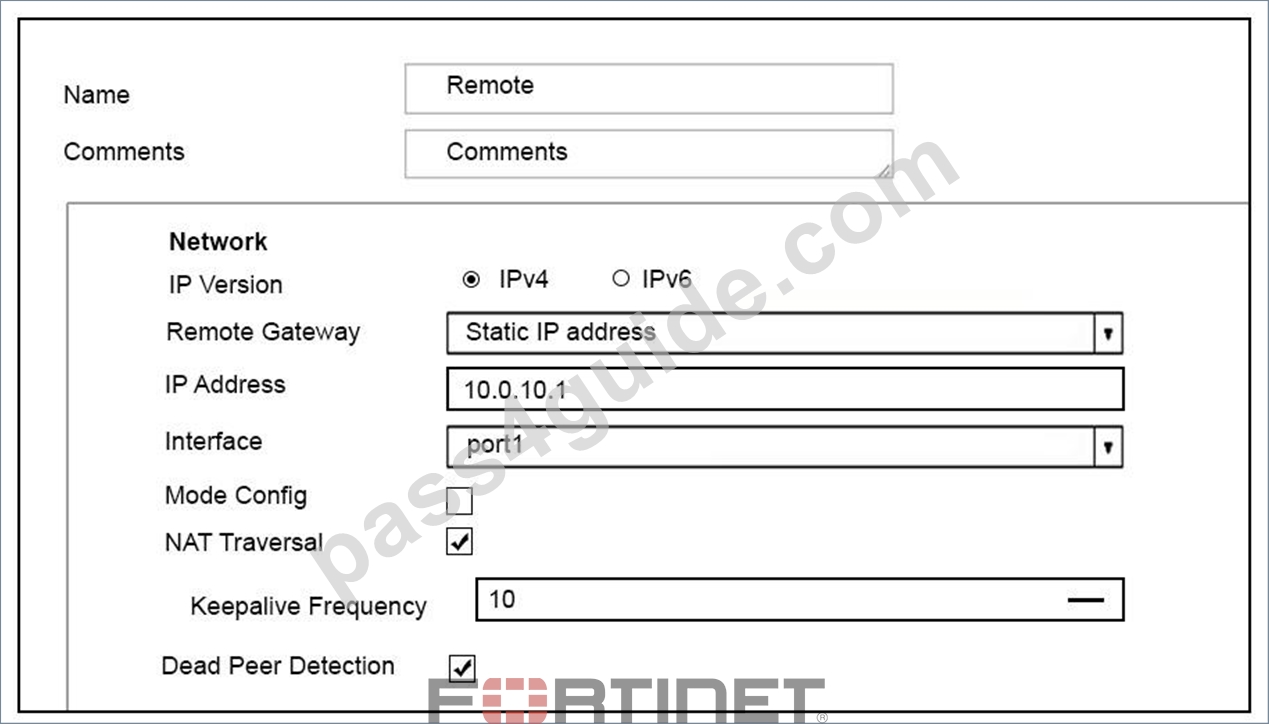
The VPN is up, and DPD packets are being exchanged between both IPsec gateways; however, traffic cannot pass through the tunnel. To diagnose, the administrator enters these CLI commands: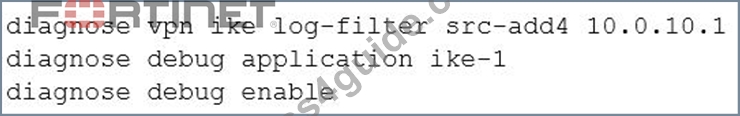
However, the IKE real time debug does not show any output. Why?
- A. The log-filter setting was set incorrectly. The VPN's traffic does not match this filter.
- B. The debug output shows phases 1 and 2 negotiations only. Once the tunnel is up, it does not show any more output.
- C. The debug shows only error messages. If there is no output, then the tunnel is operating normally.
- D. The debug output shows phase 1 negotiation only. After that, the administrator must enable the following real time debug: diagnose debug application ipsec -1.
Answer: A
NEW QUESTION # 95
Which two statements about the Security Fabric are true? (Choose two.)
- A. Only FortiGate devices with fabric-object-unification set to default will receive and synchronize global CMDB objects sent by the root FortiGate.
- B. Only the root FortiGate sends logs to FortiAnalyzer.
- C. Only the root FortiGate collects network topology information and forwards it to FortiAnalyzer.
- D. FortiGate uses FortiTelemetry protocol to communicate with FortiAnalyzer.
Answer: A,C
Explanation:
FortiGate's to Root uses FortiTelemetry (TCP-8013) FortiTelemetry is also used for FortiClient communication Root Fortigate to FortiAnalyzer uses API (TCP-443)
NEW QUESTION # 96
View the exhibit, which contains the output of a debug command, and then answer the question below.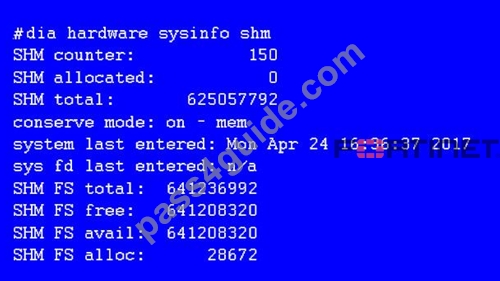
What statement is correct about this FortiGate?
- A. It is currently in system conserve mode because of high memory usage.
- B. It is currently in FD conserve mode.
- C. It is currently in kernel conserve mode because of high memory usage.
- D. It is currently in system conserve mode because of high CPU usage.
Answer: A
NEW QUESTION # 97
View the exhibit, which contains the output of a diagnose command, and then answer the question below.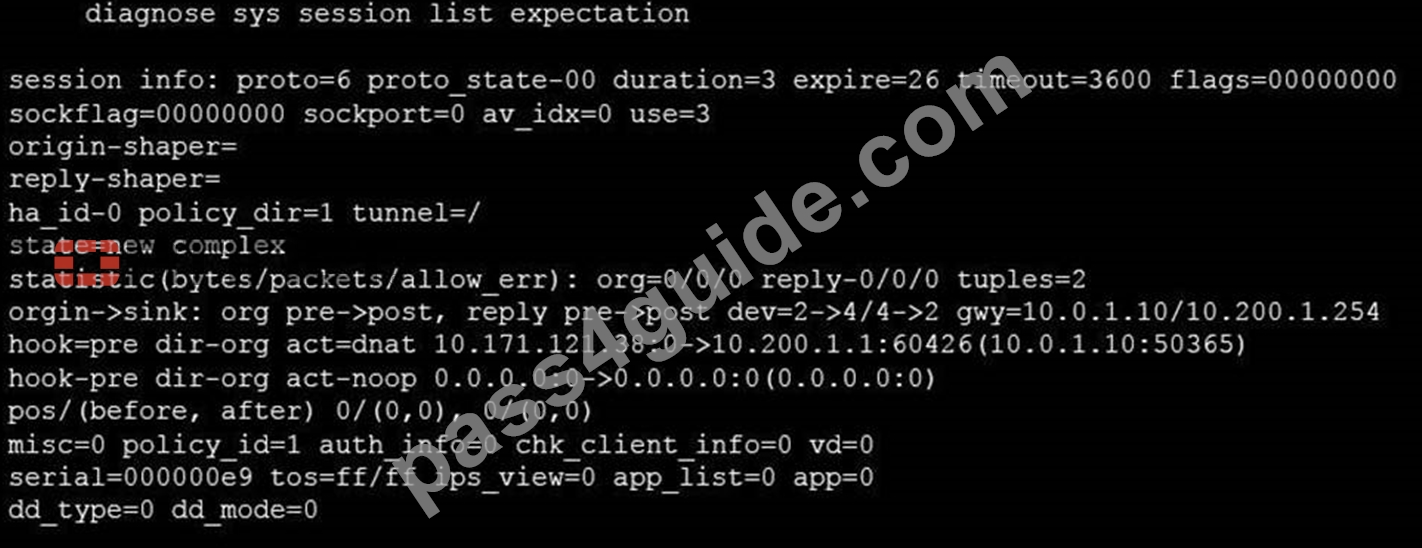
What statements are correct regarding the output? (Choose two.)
- A. This is an expected session created by a session helper.
- B. Traffic in the original direction (coming from the IP address 10.171.122.38) will be routed to the next-hop IP address 10.0.1.10.
- C. Traffic in the original direction (coming from the IP address 10.171.122.38) will be routed to the next-hop IP address 10.200.1.1.
- D. This is an expected session created by an application control profile.
Answer: A,C
NEW QUESTION # 98
Which two tasks are automated using the Install Wizard on FortiManager? (Choose two.)
- A. Importing interface mappings from managed devices
- B. Adding devices to FortiManager
- C. Previewing pending configuration changes for managed devices
- D. Installing configuration changes to managed devices
Answer: C,D
NEW QUESTION # 99
Examine the output of the 'get router info ospf interface' command shown in the exhibit; then answer the question below.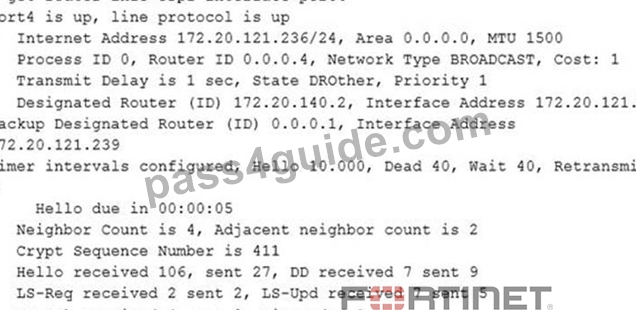
Which statements are true regarding the above output? (Choose two.)
- A. The port4 interface is connected to the OSPF backbone area.
- B. There are at least 5 OSPF routers connected to the port4 network.
- C. Two OSPF routers are down in the port4 network.
- D. The local FortiGate has been elected as the OSPF backup designated router.
Answer: A,B
NEW QUESTION # 100
Refer to the exhibit, which contains the partial output of a diagnose command.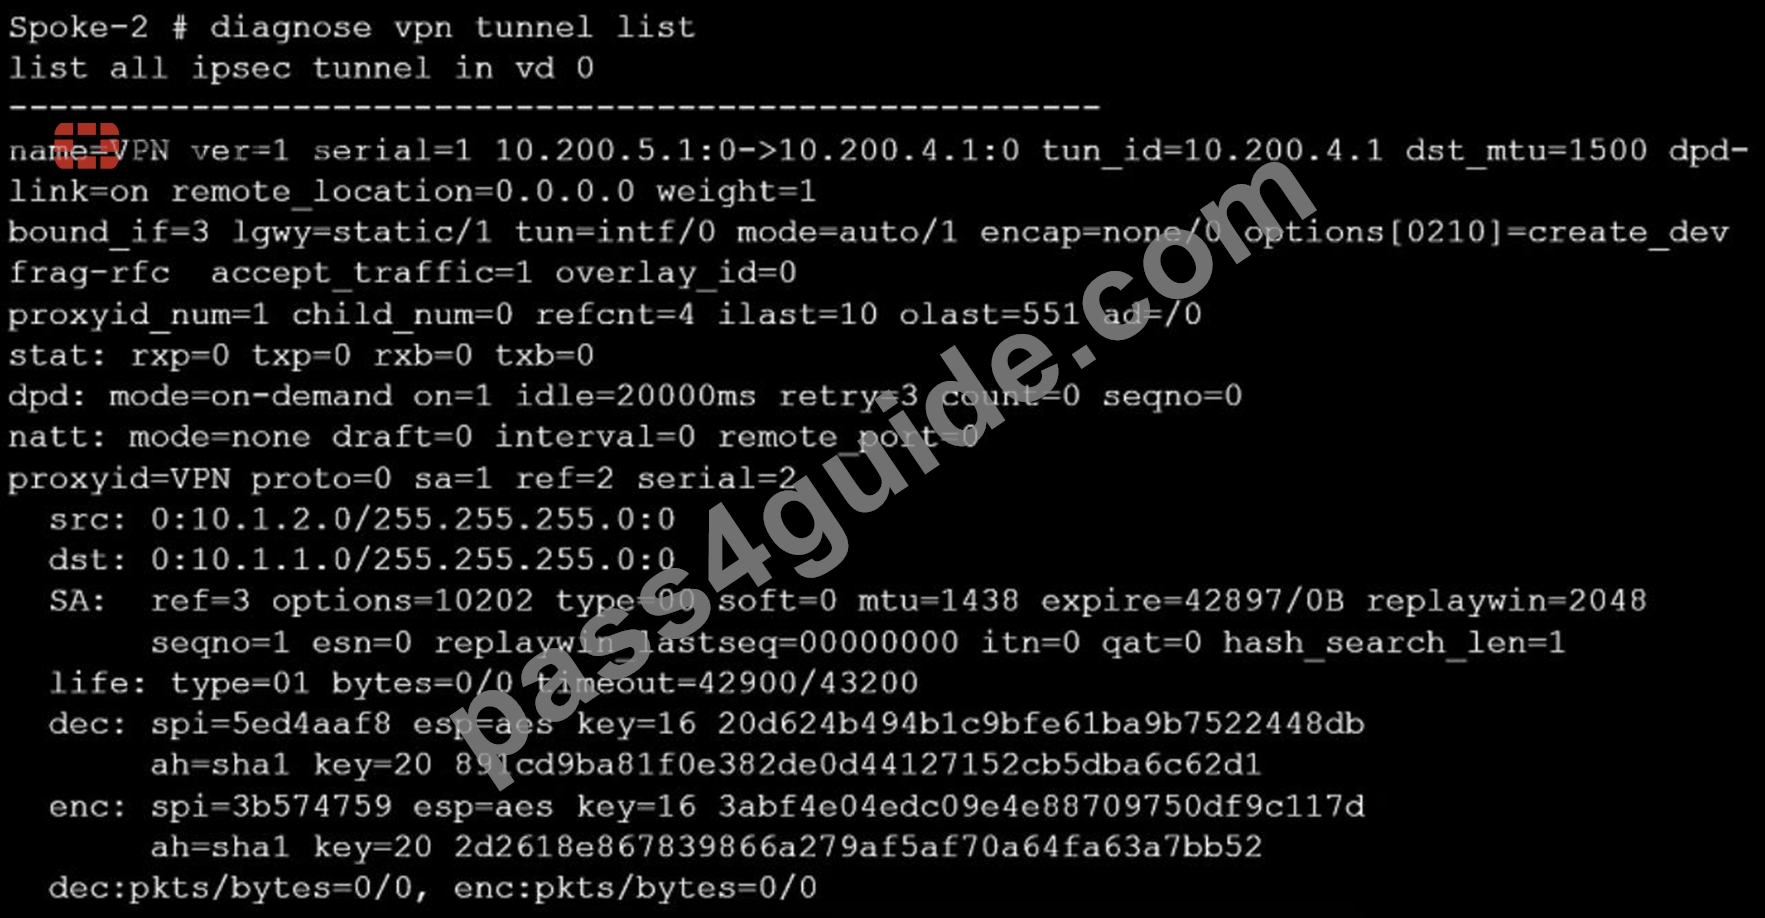
Based on the output, which two statements are correct? (Choose two.)
- A. Anti-replay is enabled.
- B. The remote gateway has quick mode selectors containing a destination subnet of 10.1.2.0/24.
- C. DPD is disabled.
- D. The remote gateway IP is 10.200.5.1.
Answer: A,B
Explanation:
Enterprise_Firewall_7.0_Study_Guide-Online.pdf p 427, 444
Since the local subnet is 10.1.2.0/24, the remote gateway has the destination subnet as 10.1.2.0. The remote gateway IP is 10.200.4.1. DPD is enabled (dpd-link=on)
NEW QUESTION # 101
View the exhibit, which contains an entry in the session table, and then answer the question below.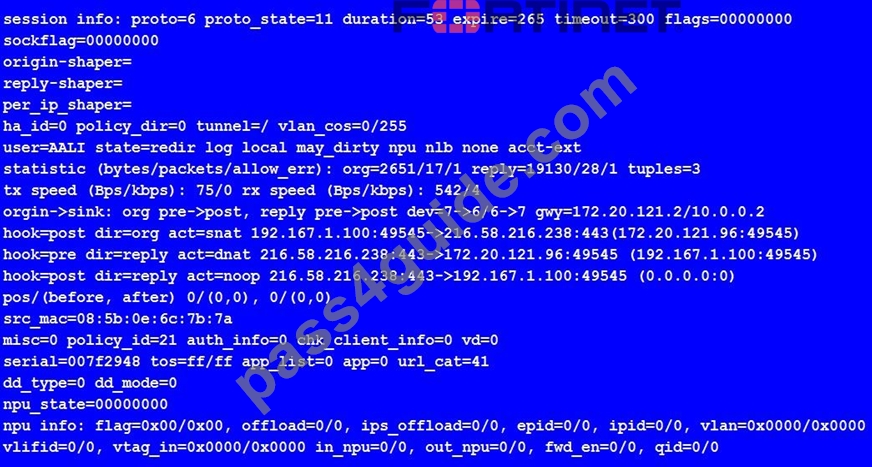
Which one of the following statements is true regarding FortiGate's inspection of this session?
- A. FortiGate applied explicit proxy-based inspection.
- B. FortiGate applied proxy-based inspection.
- C. FortiGate applied flow-based inspection.
- D. FortiGate forwarded this session without any inspection.
Answer: B
Explanation:
https://kb.fortinet.com/kb/viewContent.do?externalId=FD30042
NEW QUESTION # 102
Which of the following statements are correct regarding application layer test commands? (Choose two.)
- A. They are used to filter real-time debugs.
- B. Some of them can be used to restart an application.
- C. They display real-time application debugs.
- D. Some of them display statistics and configuration information about a feature or process.
Answer: B,D
Explanation:
Application layer test commands don't display info in real time, but they do show statistics and configuration info about a feature or process. You can also use some of these commands to restart a process or execute a change in its operation.
NEW QUESTION # 103
View the exhibit, which contains the partial output of an IKE real-time debug, and then answer the question below.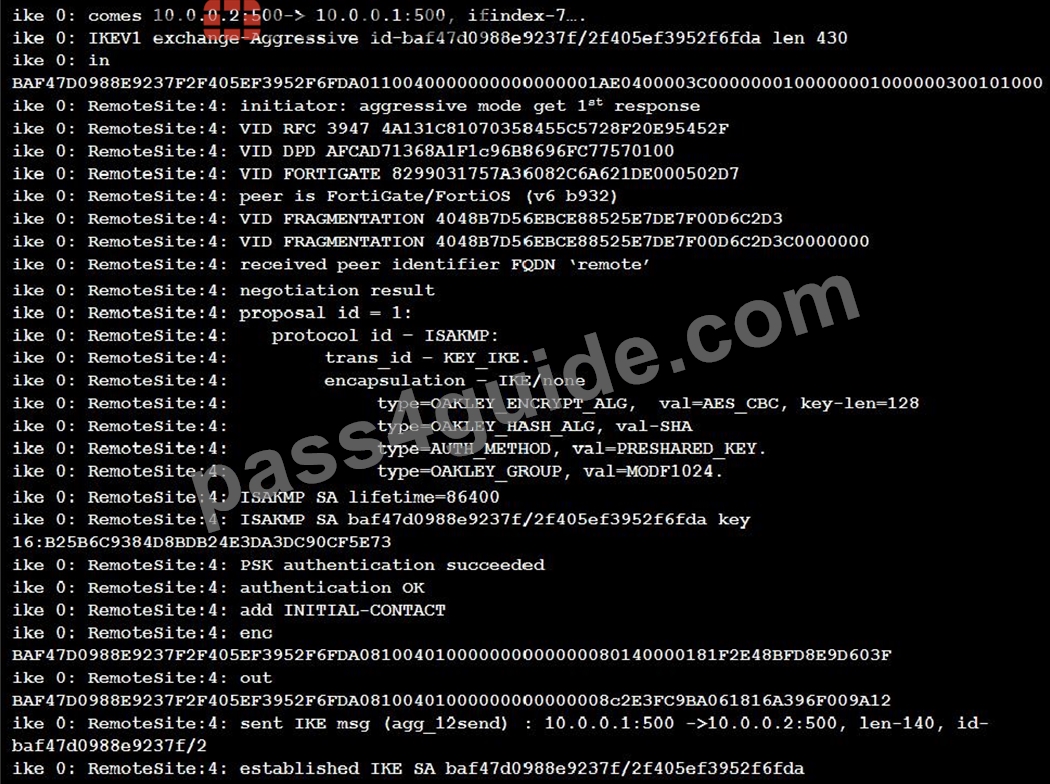
Which statements about this debug output are correct? (Choose two.)
- A. The remote gateway IP address is 10.0.0.1.
- B. The negotiation is using AES128 encryption with CBC hash.
- C. It shows a phase 1 negotiation.
- D. The initiator has provided remote as its IPsec peer ID.
Answer: C,D
NEW QUESTION # 104
An administrator has configured a dial-up IPsec VPN with one phase 2, extended authentication (XAuth) and IKE mode configuration. The administrator has also enabled the IKE real time debug:
diagnose debug application ike-1
diagnose debug enable
In which order is each step and phase displayed in the debug output each time a new dial-up user is connecting to the VPN?
- A. Phase1; XAuth; phase 2; IKE mode configuration.
- B. Phase1; XAuth; IKE mode configuration; phase2.
- C. Phase1; IKE mode configuration; phase 2; XAuth.
- D. Phase1; IKE mode configuration; XAuth; phase 2.
Answer: B
Explanation:
https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-ipsecvpn-54/IPsec_VPN_Concepts/IKE_Packet_Processing.htm
NEW QUESTION # 105
......
NSE7_EFW-7.0 Exam Questions: Free PDF Download Recently Updated Questions: https://torrentvce.pass4guide.com/NSE7_EFW-7.0-dumps-questions.html